p95 response time, after the fix
0.42s
31 days agoToday
The same load test, after the fix
Sample audit app, 500 sign-ins a minute. Missing indexes, a cache and a rate limit took p95 from 2.8 s (red) to 0.4 s (navy).
Security & scale audit
You moved fast with Lovable, Bolt, v0, Replit or Cursor, and now real customers use it. We find the leaks before someone else does, fix them at a fixed price, and help you scale without a rewrite you didn't need.
It works on screen. AI tools are excellent at what you can see and inconsistent at what you can't: who may read which row, where keys live, what happens when 500 people log in at once.
Log stream completed.
Database tables open to logged-out visitors
Secret keys shipped inside the browser bundle
Admin pages without a role check
No backups, or backups nobody has restored
Every fix breaks something else, because nothing is tested
// Runs in the browser, shipped to every visitor
const db = createClient(URL, SERVICE_ROLE_KEY)
const { data } = await db.from('bookings').select('*')

// No row-level policy on 'bookings'.
// Anyone who opens dev tools can read every booking
// and reuse the key to change them.
Illustration of the most common pattern behind incidents like CVE-2025-48757.
2.8 s 0.4 s
Slowest 5% of requests in the sample app, before and after the fix, under the same 500-user load test.
Every fix ships through tests and review, then we run the same load test as the audit. You see the before and after on one chart, and the numbers go into the signed report.
p95 response time, after the fix
Sample audit app, 500 sign-ins a minute. Missing indexes, a cache and a rate limit took p95 from 2.8 s (red) to 0.4 s (navy).
Eight questions. Your answers stay in your browser.
50
out of 100
Medium risk
There are gaps an attacker would look for first. An audit tells you which ones matter and what they cost to close.
0/8 answered. “Not sure” counts as half risk. This is a self-check, not an audit.
Book a Security & Scale AuditUS$490–990
Start here. Data access rules, keys, auth and admin routes; dependencies, backups and rate limits; a load test against your expected traffic; and a plain-English report with a fixed-price fix plan.
from US$1,500
The most common next step. We fix every critical and high finding, add tests around login, data and payments, set up backups we have restored, then re-scan and sign the report.
from US$4,900
When it has outgrown its first build. The same features on a proper Laravel architecture, your data migrated and users kept, the audit fee credited in full, and the code and hosting in your name.
Prices in USD, fixed before we start. Proposals can be fixed in CAD or NZD.
Day 0
We sign an NDA and you authorise the audit in writing. We never test anything you don't own.
Day 1
Temporary read-only access to your code and a copy of your database. No passwords by email.
Days 2–4
A senior engineer works through access rules, keys, auth, dependencies and traffic.
Day 5
Severity-ranked findings in plain English, with a fixed price for each fix. Access revoked.
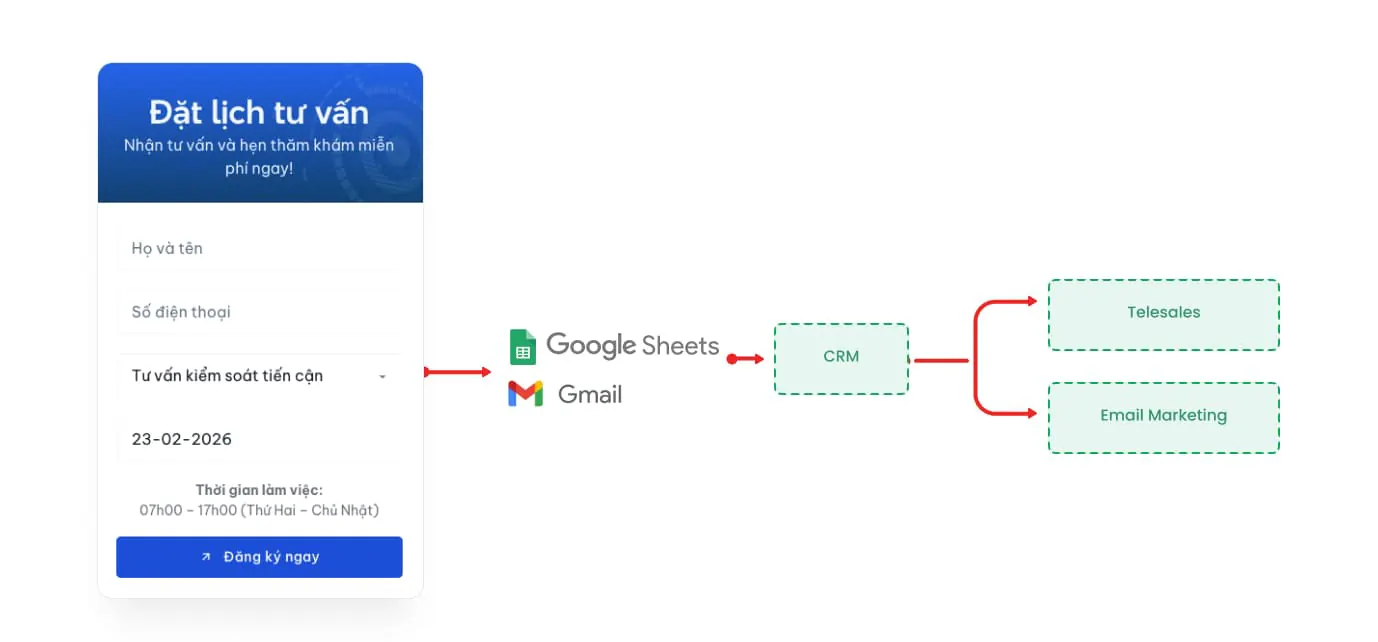
InterGreat's campaign page takes 4,000 leads every two months and hands each one to the CRM in about a second. Truong Phuc's booking forms feed telesales the same way. The engineers who audit your app are the ones who run them.
Book an audit. If we find nothing critical, you get a clean report you can show customers and insurers.
Book a free 30-min call No pressure. No generic pitch. Just a useful conversation.